

+49 800 / 27 00 001
We are thrilled to serve you
Select your language
| Mo-Th.: | 08:00 - 18:00 |
| Friday: | 08:00 - 14:00 |
External ICT Risk Manager or ICT Risk Controller
Effective ICT risk management is an essential prerequisite for the digital operational resilience of a financial entity. DORA requires a sound, comprehensive and documented ICT risk management framework with clearly defined roles, responsibilities and control structures. The management body must define, approve and oversee this framework and retains overall responsibility for it.
Depending on your organisational structure, we can support you either as an external ICT Risk Manager or by supporting the ICT risk control function as an external ICT Risk Controller.
What is the difference?
DORA does not prescribe a function specifically entitled “ICT Risk Manager”. However, for the standard ICT risk management framework, DORA requires an appropriately independent ICT risk control function. As the Regulation does not provide a detailed description of each individual role, the specific allocation of responsibilities must be adapted to the entity’s business and governance model.
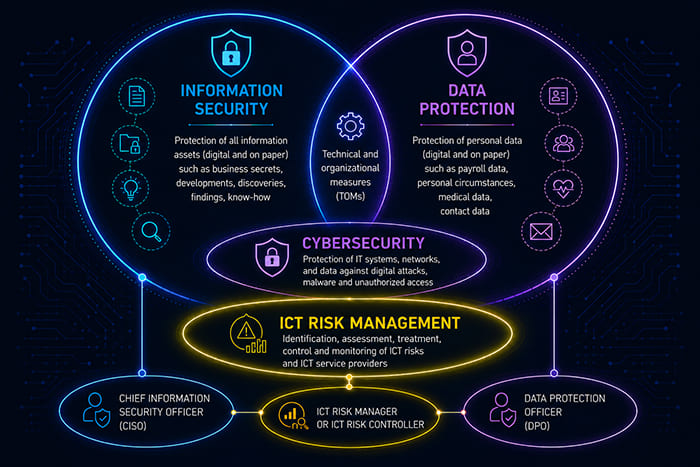
The ICT Risk Manager primarily performs operational and coordinating tasks. This role identifies and assesses ICT risks, develops appropriate measures, coordinates their implementation and consolidates information from IT, information security, business continuity and ICT third-party risk management.
The ICT Risk Controller performs a more independent control and oversight function. This role reviews and challenges risk assessments, monitors compliance with defined requirements, evaluates the effectiveness of measures and reports independently to the management body.
Internal audit must remain separate from both functions and serves as an additional independent level of assurance. DORA requires an appropriate separation between operational ICT risk management, the ICT risk control function and internal audit.

Our services
Depending on the agreed role model, we can support you with:
- establishing and maintaining the ICT risk management framework
- identifying, analysing and assessing ICT risks
- defining risk tolerance levels and assessing residual risks
- creating and maintaining the ICT risk inventory
- monitoring measures and identified findings
- developing key risk indicators and early-warning indicators
- supporting ICT third-party risk management
- coordinating incident management, resilience testing and business continuity arrangements
- preparing regular reports for the management body
- preparing for internal and external audits
Where permitted by the applicable sector-specific governance and outsourcing requirements, certain activities relating to the review of compliance with ICT risk management requirements may be performed externally. However, responsibility remains with the financial entity.
Whether a separate ICT risk control function is required depends on the applicable DORA framework. As a general rule, this function is not required for microenterprises or entities applying the simplified ICT risk management framework under Article 16 DORA.
Together with you, we develop a role model that is appropriate for your organisation and ensures the necessary independence, expertise and effective oversight.
Address
Frommel Datenschutz GmbH
Akazienstr. 6a
61352 Bad Homburg
Germany
Contact
Phone: +49 6172 / 1710179
Fax: +49 6172 / 1714896
WhatsApp: +49 6172 / 4954596
E-Mail: datenschutz@frommel.com
Web: datenschutz.frommel.com
Opening hours
| Mo.-Th.: | 08:00 a.m. – 06:00 p.m. |
| Friday: | 08:00 a.m. – 02:00 p.m. |
| Saturday: | on appointment |
Our strengths
- Free and non-binding initial consultation
- Competent, individual and ongoing support
- Practical and illustrative use cases
- Pragmatic solutions
- Many years of experience