

+49 800 / 27 00 001
We are thrilled to serve you
Select your language
| Mo-Th.: | 08:00 - 18:00 |
| Friday: | 08:00 - 14:00 |
Individual Consulting on ICT Risk Management under DORA

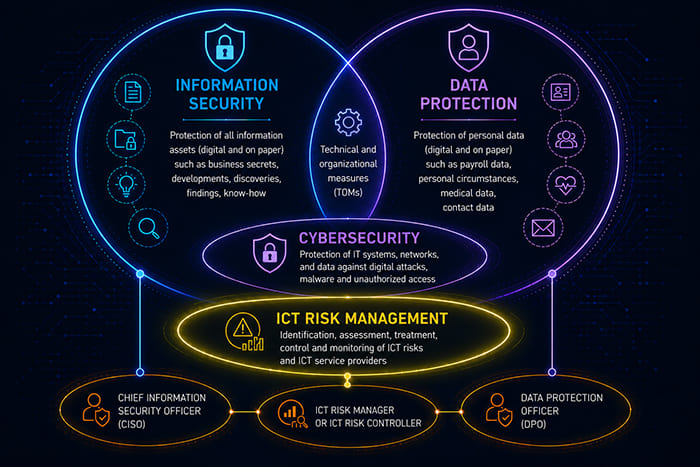
DORA establishes comprehensive requirements for the management of ICT risks and the digital operational resilience of financial entities. In addition to the ICT risk management framework, the Regulation covers areas such as ICT-related incident management, digital operational resilience testing and ICT third-party risk management.
We support you with individual questions or with the complete implementation and further development of your DORA structures. In doing so, we take into account the size and risk profile of your organisation as well as the nature, scale and complexity of your business activities.
Our consulting services
Our services may include:
- assessing whether DORA applies to your organisation and determining the applicable ICT risk management framework
- establishing an appropriate governance and role structure
- developing the digital operational resilience strategy
- preparing policies, guidelines and process descriptions
- identifying and classifying information and ICT assets
- mapping ICT assets to business processes and functions
- developing a methodology for identifying and assessing ICT risks
- defining risk tolerances, indicators and reporting channels
- establishing ICT incident management, including classification and notification procedures
- developing ICT business continuity, response and recovery plans
- planning and documenting digital operational resilience tests
- establishing ICT third-party risk management
- supporting the register of information, contract reviews and exit strategies
- preparing management reports and decision-making documents
DORA and the supplementary Regulatory Technical Standards specify the required methods, processes, policies and control mechanisms in greater detail. These include, for example, ICT asset management, information security, encryption, network security, ICT project management and physical security measures.
Structured approach
Our consulting services usually follow four stages:
- Current-state assessment: Review of existing structures, processes and documentation
- Evaluation: Identification of gaps, risks and opportunities for improvement
- Implementation: Development and introduction of appropriate measures and documentation
- Further development: Review of effectiveness and regular updating
We can support the complete implementation process or assist your internal teams through coaching and professional quality assurance.
Our objective is to establish practical ICT risk management that meets regulatory requirements and can be effectively integrated into your existing business and decision-making processes.
Address
Frommel Datenschutz GmbH
Akazienstr. 6a
61352 Bad Homburg
Germany
Contact
Phone: +49 6172 / 1710179
Fax: +49 6172 / 1714896
WhatsApp: +49 6172 / 4954596
E-Mail: datenschutz@frommel.com
Web: datenschutz.frommel.com
Opening hours
| Mo.-Th.: | 08:00 a.m. – 06:00 p.m. |
| Friday: | 08:00 a.m. – 02:00 p.m. |
| Saturday: | on appointment |
Our strengths
- Free and non-binding initial consultation
- Competent, individual and ongoing support
- Practical and illustrative use cases
- Pragmatic solutions
- Many years of experience