

+49 800 / 27 00 001
We are thrilled to serve you
Select your language
| Mo-Th.: | 08:00 - 18:00 |
| Friday: | 08:00 - 14:00 |
Tailored Information Security Consulting
Every organisation has different business processes, information assets, IT systems and security risks. Effective information security management must therefore reflect the actual organisation and should not be based solely on generic templates.
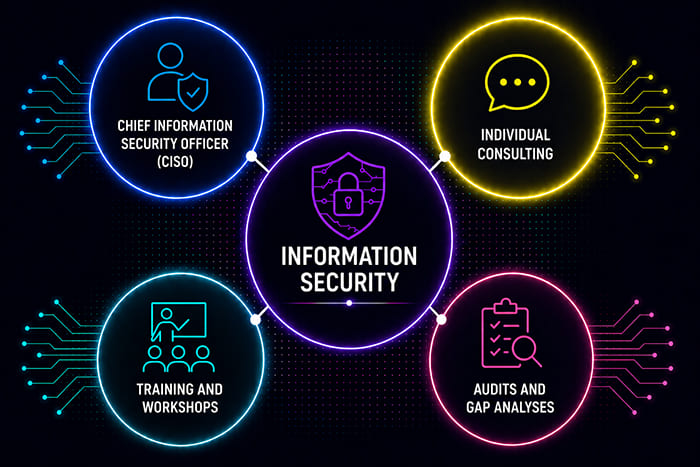
We support you in establishing, reviewing and further developing your information security management arrangements – from individual questions to the complete implementation of an ISMS in accordance with ISO/IEC 27001.
Our consulting services
Our services may include:
- supporting the assessment of whether NIS2 and the German BSI Act apply to your organisation
- assessing existing information security structures
- defining the scope of the ISMS
- identifying relevant business processes, information and IT assets
- conducting protection requirements assessments and risk analyses
- developing an appropriate risk treatment approach
- preparing the Statement of Applicability
- developing policies, guidelines and process descriptions
- establishing an information security incident management process
- designing access control, vulnerability and supplier management processes
- developing business continuity, backup and recovery arrangements
- establishing indicators, reporting channels and control mechanisms
- supporting registration and incident notification processes under NIS2 and the German BSI Act
- preparing for internal audits and certification audits
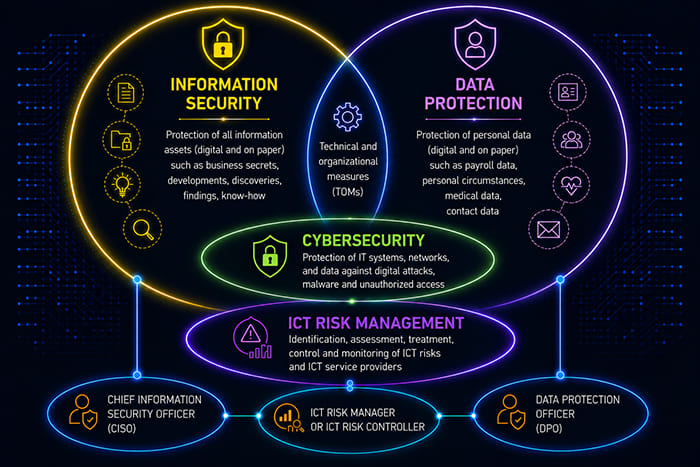
For essential and important entities, the German BSI Act requires appropriate, proportionate and effective risk-management measures. These measures must be based on a risk analysis, documented and regularly reviewed for effectiveness.
Structured approach
Our consulting services usually follow four stages:
- Current-state assessment: We analyse existing structures, processes and documentation.
- Evaluation: We identify risks, gaps and opportunities for improvement.
- Implementation: We work with you to develop appropriate measures and documentation.
- Continual improvement: We review effectiveness and support the ongoing development of the ISMS.
We can accompany the entire implementation process or support your internal teams through coaching, templates and professional quality assurance.
Our objective is to establish clear and practical information security management that meets regulatory requirements and can be permanently integrated into your business processes.
Address
Frommel Datenschutz GmbH
Akazienstr. 6a
61352 Bad Homburg
Germany
Contact
Phone: +49 6172 / 1710179
Fax: +49 6172 / 1714896
WhatsApp: +49 6172 / 4954596
E-Mail: datenschutz@frommel.com
Web: datenschutz.frommel.com
Opening hours
| Mo.-Th.: | 08:00 a.m. – 06:00 p.m. |
| Friday: | 08:00 a.m. – 02:00 p.m. |
| Saturday: | on appointment |
Our strengths
- Free and non-binding initial consultation
- Competent, individual and ongoing support
- Practical and illustrative use cases
- Pragmatic solutions
- Many years of experience