

+49 800 / 27 00 001
We are thrilled to serve you
Select your language
| Mo-Th.: | 08:00 - 18:00 |
| Friday: | 08:00 - 14:00 |
External Chief Information Security Officer (CISO)
Information security is not a one-off technical task, but a continuous management process. An information security management system, or ISMS, provides the structures required to protect information systematically and manage risks appropriately. ISO/IEC 27001 defines the requirements for establishing, implementing, maintaining and continually improving such a management system.
As your external Chief Information Security Officer (CISO), we coordinate your information security management activities, advise executive management, support the implementation of appropriate measures and provide regular reports on the status of information security.
Our services
Depending on your organisation and the agreed scope of services, we support you with:
- establishing, operating and continually improving the ISMS
- defining security objectives, roles and responsibilities
- preparing and maintaining policies, guidelines and process descriptions
- identifying and assessing information security risks
- planning and monitoring appropriate security measures
- coordinating security incidents and improvement measures
- involving IT service providers, suppliers and other contractors
- developing indicators and management reports
- planning training and awareness activities
- preparing for internal audits and certification audits
- supporting compliance with ISO/IEC 27001, NIS2 and the German BSI Act (BSIG)

Clear roles and responsibilities
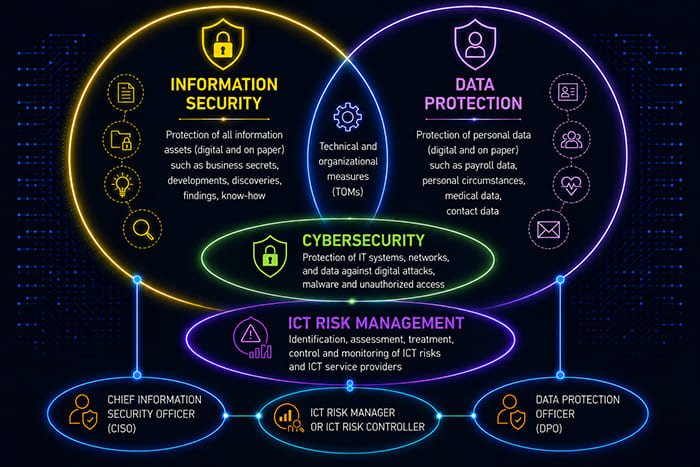
The CISO coordinates, advises and monitors. The operational implementation of technical and organisational measures remains the responsibility of the relevant departments, IT teams and process owners. Overall responsibility for information security remains with executive management.
To avoid conflicts of interest, the CISO should operate with an appropriate degree of independence and report directly to executive management. The specific mandate, information rights, reporting channels and confidentiality requirements are clearly defined at the beginning of the engagement.
An external CISO is particularly suitable for organisations that do not maintain their own specialised information security function or wish to complement their existing information security management with independent expertise.
We provide ongoing, temporary or supplementary support for your information security management.
Address
Frommel Datenschutz GmbH
Akazienstr. 6a
61352 Bad Homburg
Germany
Contact
Phone: +49 6172 / 1710179
Fax: +49 6172 / 1714896
WhatsApp: +49 6172 / 4954596
E-Mail: datenschutz@frommel.com
Web: datenschutz.frommel.com
Opening hours
| Mo.-Th.: | 08:00 a.m. – 06:00 p.m. |
| Friday: | 08:00 a.m. – 02:00 p.m. |
| Saturday: | on appointment |
Our strengths
- Free and non-binding initial consultation
- Competent, individual and ongoing support
- Practical and illustrative use cases
- Pragmatic solutions
- Many years of experience