

+49 800 / 27 00 001
We are thrilled to serve you
Select your language
| Mo-Th.: | 08:00 - 18:00 |
| Friday: | 08:00 - 14:00 |
Audits and Gap Analyses under DORA
An ICT risk management framework must be reviewed and updated regularly and continuously improved on the basis of experience and lessons learned. DORA also requires regular internal audits by auditors with appropriate expertise and independence, as well as a formal process for monitoring and remediating significant findings. Through our audits and gap analyses, we assess the extent to which the requirements of DORA and the supplementary Regulatory Technical Standards have been implemented and whether the established measures are operating effectively in practice.
Possible areas of assessment
Depending on the agreed scope, we review areas including:
- governance, roles and responsibilities
- involvement and oversight by the management body
- the ICT risk management framework and digital operational resilience strategy
- the ICT risk inventory and risk assessment methodology
- classification of information and ICT assets
- protection, prevention and detection measures
- ICT incident management, classification and notification procedures
- ICT business continuity, backup and recovery
- digital operational resilience testing
- ICT third-party risk management
- the register of information and contractual minimum requirements
- training and awareness programmes
- reporting, indicators and action tracking
- regular reviews and continuous improvement
The assessment may cover the standard ICT risk management framework under Articles 5 to 15 DORA or, where applicable, the simplified framework under Article 16 DORA. The supplementary Regulatory Technical Standards are also included in the assessment criteria.
Difference between an audit and a gap analysis
During an audit, we assess against defined criteria whether the required policies, processes and measures have been appropriately implemented and are operating effectively.
A gap analysis compares the current state with the applicable regulatory target state. It is particularly suitable for preparing a DORA implementation project, assessing the organisation’s current level of maturity or planning further measures.
The assessment may include document reviews, interviews, sample-based testing and the evaluation of available evidence.
Clear and actionable results
Depending on the agreed scope, you will receive:
- a structured overview of the requirements assessed
- identified strengths and opportunities for improvement
- identified deviations and documentation gaps
- an assessment of their criticality
- specific recommendations for action
- a prioritised action plan
- an executive summary upon request
Before the assessment begins, we agree on the assessment criteria, the required level of independence and any potential conflicts of interest. Consulting and audit activities are separated appropriately to avoid improper self-review.
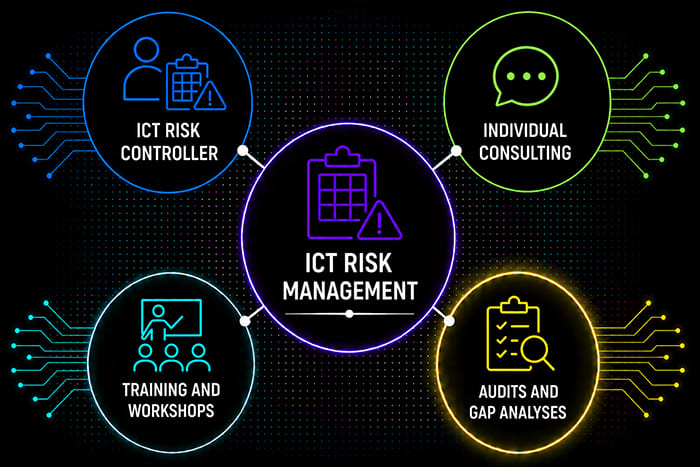
Our audits and gap analyses provide transparency regarding your current level of DORA implementation and identify the areas in which targeted improvements are required.
Address
Frommel Datenschutz GmbH
Akazienstr. 6a
61352 Bad Homburg
Germany
Contact
Phone: +49 6172 / 1710179
Fax: +49 6172 / 1714896
WhatsApp: +49 6172 / 4954596
E-Mail: datenschutz@frommel.com
Web: datenschutz.frommel.com
Opening hours
| Mo.-Th.: | 08:00 a.m. – 06:00 p.m. |
| Friday: | 08:00 a.m. – 02:00 p.m. |
| Saturday: | on appointment |
Our strengths
- Free and non-binding initial consultation
- Competent, individual and ongoing support
- Practical and illustrative use cases
- Pragmatic solutions
- Many years of experience